the agentic harness for security teams
Meet ZERO — an autonomous cyber environment that brings models, agent swarms, and tools under your command to test, trace, and verify your systems.
request accessblackbit.zero — trailer
film — watch first
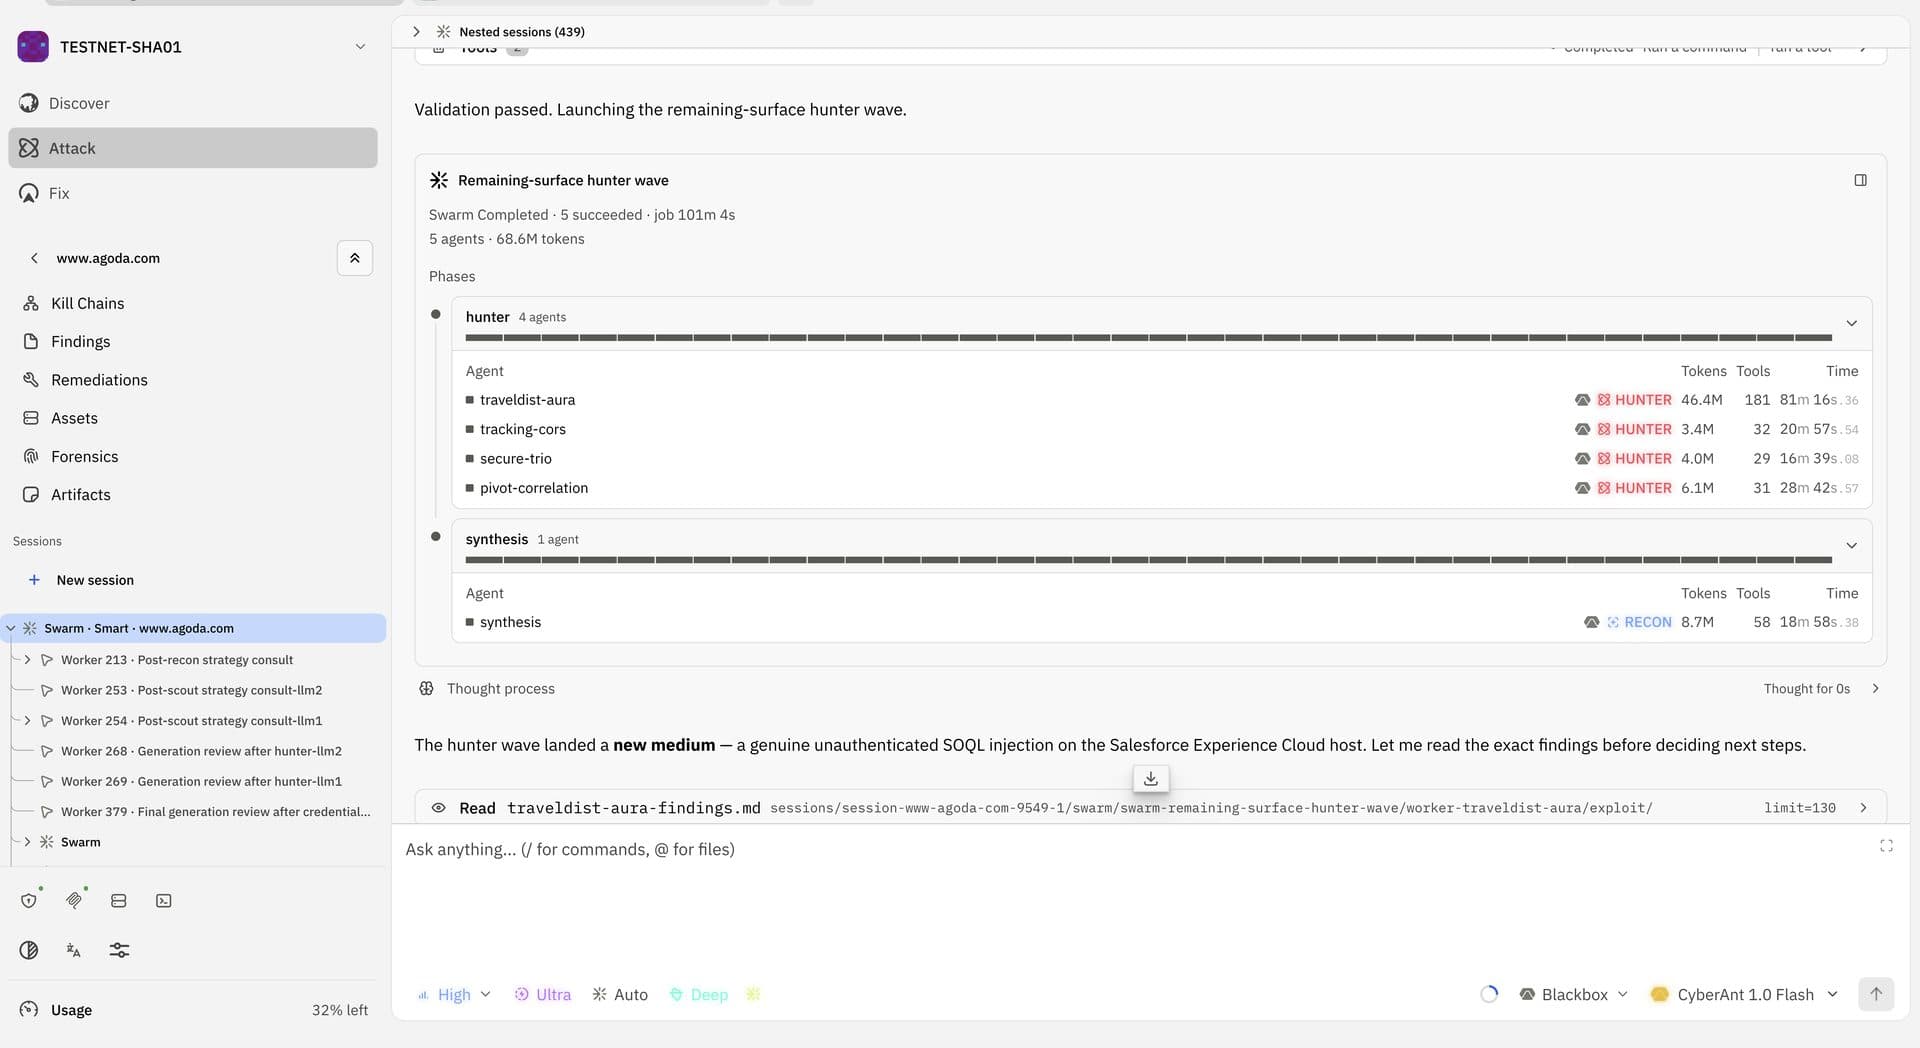
film — trailer
watch zero in action
The harness in motion — from a single command to swarm, forensic trace, and a fix you can retest.
built by engineers previously at
harness capabilities
scoped autonomy
Define authorized domains, repositories, clearance IDs, and operational limits before any agent runs. Pause, redirect, or abort in real time.
multi-agent swarms
Orchestrate concurrent reconnaissance, analysis, and exploitation sub-agents across complex attack surfaces from a single operator command.
forensic trace map
Inspect every model call, tool execution, and discovered weakness on a live signal graph with full evidence from initial recon to verification.
continuous retesting
Turn point-in-time assessments into repeatable verification. Automatically re-run targeted checks as your code and infrastructure change.
01 — how it works
04 phases — machine tempo
scope
Set authorized domains, repositories, clearance IDs, and operational guardrails before any assessment begins.
task
Select your model route on the VOID gateway and assign specialized Recon, Scout, or Hunter agents to the objective.
execute
Coordinate autonomous agent swarms that enumerate surfaces, test weaknesses, and log verifiable evidence in isolated sandboxes.
verify
Inspect the forensic trace map, validate remediation patches, and re-run targeted checks as your systems evolve.
02 — agent classes
03 classes — specialized roles
autonomous agent classes
Specialized agents for each stage of an assessment — from rapid surface mapping to multi-day vulnerability research, composed under your command.
reconag-01enumeration
Fast attack-surface enumeration, asset discovery, and dependency mapping across authorized domains and repositories.
scope
domains
depth
surface
tempo
continuous
scoutag-02analysis
Targeted vulnerability analysis, code review, and configuration testing across web applications, APIs, identity, and cloud.
scope
apps + apis
depth
targeted
tempo
on-change
hunterag-03research
Long-horizon multi-swarm orchestration for deep exploit chains, binary reverse engineering, and zero-day research.
scope
binaries
depth
deep trace
tempo
multi-day
03 — engagement controls
intensity + depth — set before send
how hard, how deep
Two controls, set before the first send. Intensity decides how far exploitation goes. Depth decides how thoroughly recon maps the estate.
intensity — medium / max / ultra
mediumin-01kill-chain
Follow the attack path to one agreed objective. The engagement finishes when that objective is proven, or the authorized surface is exhausted.
- scope
- objective
- method
- kill-chain
- finish
- one proof
maxin-02full compromise
Work the whole authorized surface. Every declared objective is proven, or recorded as blocked with a reason before the engagement can close.
- scope
- full surface
- method
- compromise
- finish
- every path
ultrain-03flywheel
Keep going after the first proof. New findings raise the priority board, and independent paths are delivered across successive rounds.
- scope
- full surface
- method
- rounds
- finish
- multi-path
depth — shallow / deep / zero-day
shallowdp-01lighter
A lighter pass over the authorized estate — fewer pages, a shallower crawl, and a smaller wordlist before the next phase.
- crawl
- 15 pages
- depth
- 1 level
- wordlist
- small
deepdp-02default
The default. Thorough recon with a deeper crawl, larger wordlists, and parallel analysts mapping the estate before testing begins.
- crawl
- 30 pages
- depth
- 2 levels
- wordlist
- large
zero-daydp-03research
Deep recon plus coverage-guided fuzzing — Foundry for contracts, AFL++ for native binaries. Research mode does not guarantee a new vulnerability.
- recon
- deep
- fuzz
- guided
- budget
- 8 hours
04 — capabilities & tools
08 sectors — 188 tools
what the agents can do
Start from a live system, source code, both, or an Android artifact. Engagements run across web, source, web3, wireless, cameras, and industrial networks.
sc-01web applications & apis
Map the exposed surface, then test inputs, access control, and business workflows across pages, APIs, and authentication flows.
surface
web-http
start
live
proof
request
sc-02source & delivery
Review a repository without a live target — secrets, dependencies, containers, serverless functions, and how jobs obtain cloud access.
surface
app-source
start
source
proof
static
sc-03identity & cloud
Follow how one account becomes broader access — Active Directory, Kerberos, sessions, and supported AWS, Azure, and Kubernetes paths.
surface
identity
start
combined
proof
path
sc-04android applications
Inspect APKs and supported bundles, then test in the managed emulator. Dynamic testing is local and Android-only — not iOS or physical devices.
surface
android
start
artifact
runtime
emulator
sc-05blockchain & contracts
Map contracts, run analyzer leads, and replay supported Ethereum cases. Analyzer output is a lead, not proof, and wallets do not broadcast transactions.
surface
web3
start
contract
proof
replay
sc-06fuzz & binaries
Feed unexpected inputs, group crashes, and keep the evidence needed to reproduce them. Zero-day mode does not guarantee a new vulnerability.
surface
research
engine
afl++
proof
repro
sc-07industrial & cameras
Read-oriented discovery of supported industrial networks, plus ONVIF and RTSP cameras. No process writes, controller changes, or OPC UA assessment.
surface
ot
camera
lan
mode
read-only
sc-08assisted workflows
Prepare tests for AI applications, Wi-Fi and Bluetooth reconnaissance, privileged-access systems, backups, printers, and artifact signing. Execution still needs the operator and the right tools.
surface
wifi-rf
mode
assisted
proof
prepared
planning & methodology29
artifact
01
clone source
02
closeout
03
attack plan
04
plan sync
05
intel
06
gate
07
loot
08
replay
09
session git
10
index
11
finalize
12
report
13
reduce
14
patch deliverable
15
tool families
16
programs
17
research
18
recon plan
19
ensure tools
20
scope check
21
agent budget
22
coverage note
23
finding
24
web model
25
web scenario
26
methodology status
27
detection run
28
emulate actor
29
recon & discovery27
live recon
01
http
02
http triage
03
port scan
04
content disc
05
archive urls
06
fingerprint
07
osint
08
shodan
09
recon dns
10
schema
11
cdn map
12
waf probe
13
rate probe
14
auth map
15
shadow it
16
recon mobile
17
mobile device
18
mobile control
19
mobile traffic
20
recon delta
21
recon registry
22
recon serverless
23
ot
24
camera
25
nuclei
26
git history
27
web vulnerabilities22
vuln sqli
01
vuln xss
02
vuln ssrf
03
vuln idor
04
vuln xxe
05
vuln cors
06
vuln mass assignment
07
vuln api abuse
08
vuln websocket
09
vuln graph inject
10
vuln nosql
11
vuln csrf analyze
12
vuln hpp
13
vuln ssti
14
vuln deser
15
vuln csv
16
vuln race
17
vuln stateful fuzz
18
vuln synthesize
19
oob
20
llm sec
21
vuln serverless inject
22
exploit16
exploit chain
01
exploit jwt
02
exploit ssti
03
exploit generate
04
exploit upload
05
exploit auth bypass
06
exploit pp
07
exploit dom xss
08
exploit crlf
09
exploit xpath
10
exploit ldap
11
exploit mail inject
12
hackbrowser
13
attack script
14
ebpf
15
rf
16
identity & active directory21
lateral pth
01
lateral tickets
02
persist schtask
03
persist registry
04
persist dll hijack
05
persist service
06
persist linux
07
persist k8s
08
ad gpo
09
ad laps
10
ad delegation unconstrained
11
ad sidhistory
12
ad bronzebit
13
ad spray
14
identity
15
network
16
bloodhound
17
adcs
18
kerberos
19
relay
20
delegation
21
cloud & post-exploitation22
cloud metadata
01
cloud aws pe
02
cloud azure ad
03
cloud k8s pe
04
cloud escape
05
cloud storage enum
06
cloud secrets scan
07
cloud gcp iam
08
cloud trigger abuse
09
supplychain
10
tradecraft
11
exfil proof
12
bolt
13
cipipe
14
pam
15
wif
16
backup
17
printer
18
collab hunt
19
supplychain sign
20
workflow abuse
21
c2
22
web329
web3 recon
01
web3 detect
02
web3 wallet
03
web3 slither
04
web3 halmos
05
web3 foundry
06
web3 defi
07
web3 bridge
08
web3 mempool
09
web3 mev
10
web3 nft
11
web3 solana
12
web3 anvil
13
web3 aderyn
14
web3 source tree
15
web3 decompile
16
web3 move
17
web3 cosmos
18
web3 deps
19
web3 vyper
20
web3 aa
21
web3 intent
22
web3 svm scan
23
web3 rollup
24
web3 callgraph
25
web3 tx trace
26
web3 diff
27
web3 svm harness
28
web3 economic sim
29
fuzz & crash2
fuzz
01
crash
02
defense evasion15
evasion amsi
01
evasion etw
02
evasion memory
03
evasion hollow
04
evasion doppelganger
05
evasion macro obfuscate
06
evasion ps obfuscate
07
evasion shellcode encode
08
evasion antidebug
09
evasion vm detect
10
evasion timing
11
evasion activity
12
evasion lolbin
13
evasion signed proxy
14
evasion c2 select
15
hooks5
aws hook
01
azure hook
02
kube hook
03
win hook
04
mac hook
05
Defend yourself continuously,
under your own command.
request access05 — use cases
04 workflows — autonomous defense
continuous pen testing
Run daily scoped assessments across evolving web applications, APIs, and cloud infrastructure without waiting for annual audit cycles.
scope
authorized
mode
scheduled
output
trace + poc
application & smart contract audit
Review pull requests, protocol upgrades, and critical code paths before deployment with coordinated specialist sub-agents.
scope
repositories
mode
pre-deploy
output
diff + fix
zero-day & binary research
Decompile, reverse engineer, and fuzz complex targets in isolated cloud sandboxes with long-running multi-agent swarms.
scope
sandboxed
mode
deep swarm
output
findings
remediation verification
Automatically re-run exploit traces against patched builds to verify that reported vulnerabilities are closed before release.
scope
patches
mode
retest
output
verified
06 — pricing
02 tiers — beta access
pricing
ZERO is now in beta. Access is authorized per organization — request access and we enable your seats once your team is approved.
team
$399per seat / month
For security teams running scoped, continuous testing with the full harness — every agent class, multi-agent swarms, the forensic trace map, and continuous retesting.
- access
- request access
- agents
- all classes
- billing
- per seat
enterprise
customagreed per organization
For larger organizations with custom authorization, deployment, and support requirements — scope and terms are agreed before access is enabled.
- access
- by request
- agents
- all classes
- billing
- custom
access is authorized by email
request accessCommand the swarm
on your systems
so they learn to
{defend themselves}
send us an emailauthorization required
01 — your company
Tell us the company you are from — your name, your role, and a work email we can verify.
02 — test target
Tell us the company you want to run tests for — and confirm you own those systems or have written authorization to test them.
why we ask
ZERO runs autonomous offensive agents. We authorize every organization before enabling access, so the platform cannot be used to hurt others.
platform — mac with apple silicon only
For now, ZERO runs only on Macs with an Apple silicon (M-series) chip. Intel Macs, Windows, and Linux are not supported yet.
hello@blackbit.sh
request access